A recent Wall Street Journal headline warned that AI-enabled attacks are arriving rapidly and overwhelming the internet. At the same time, another discussion asked why the predicted wave of AI hacking had not yet appeared. My answer is simple: it is already here, but much of the cybersecurity community is not seeing it.
I am not an AI evangelist. I tend to be conservative about new technology, and I still prefer practical tools that work over expensive platforms that promise transformation. That makes my conclusion more important, not less: AI is changing the cyber fight now, not at some distant point in the future.
Why the Change Is Easy to Miss
Cybersecurity has never been particularly good at detection. Many successful intrusions are never identified, and the industry’s obsession with dramatic announcements makes it difficult to separate meaningful change from marketing noise. If defenders cannot see most of what is already happening, they are unlikely to recognize immediately when the pace and character of offensive activity changes.
Historically, the first foothold into a network could happen quickly, but the next steps usually happened at human speed. An attacker might wait days, weeks, or months before returning to an access point, moving laterally, locating useful information, and acting on it. Access was often traded or sold before anyone used it. Humans remained the limiting factor.
From Human-Speed Intrusion to Machine-Speed Pivot
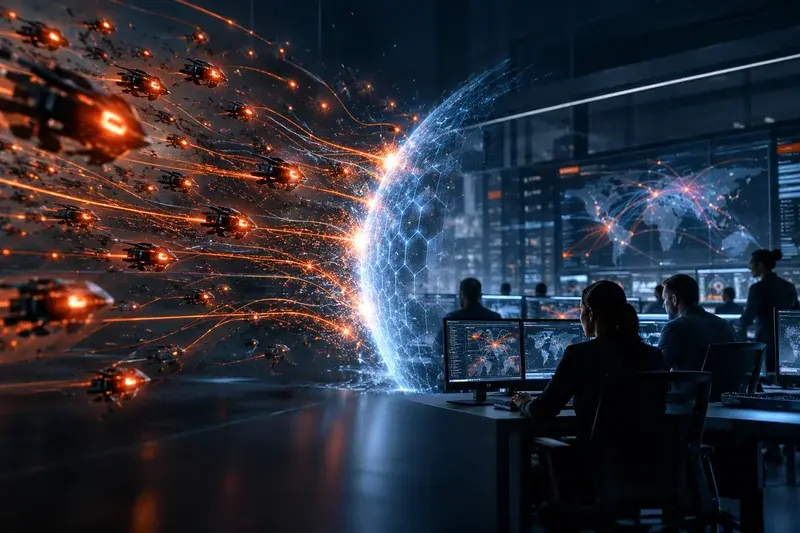
Offensive AI agents are removing that delay. They can make initial access easier, but the more consequential shift comes afterward: an agent can begin evaluating the environment, moving through complex systems, identifying valuable information, and taking action immediately after the first compromise.
That matters for ordinary criminal activity, but it is especially serious in a nation-state context. An adversary seeking intelligence, destructive access, or effects in the physical world can use machine-speed operations to establish options across a target environment before traditional defenders have finished understanding the initial alert.
The old imbalance already favored attackers. Defense teams were often outmatched, operating with incomplete visibility and delayed information. AI does not create that imbalance, but it accelerates it. Offense can now operate continuously, adapt quickly, and chain actions together at a pace that human-only response teams cannot match.
Defenders Need AI Agents Too
The first implication is straightforward: defenders need cyber defensive AI agents operating continuously. Defense Cybersecurity Group has spent the last several years developing internal AI models. ECNE, the Enhanced Cyber Neural Engine, is running on GPUs inside our FedRAMP boundary, and ECNE Blue is our research and development effort focused on defensive cyber agents.
This is not about adding an AI label to another dashboard. It is about building practical defensive systems capable of observing activity, identifying anomalies, and helping teams respond at the same speed attackers are beginning to achieve.
Prevention Alone Is Falling Further Behind
The second implication is that a prevention-first strategy is becoming even less adequate. AI agents can combine known weaknesses, adapt techniques, and find new paths through an environment faster than conventional patch-and-block processes can react. Prevention still matters, but it cannot be the center of the entire defensive model.
This has direct relevance to CMMC and other government cybersecurity frameworks. Those frameworks emphasize preventative safeguards. Their detection requirements are comparatively limited, particularly when measured against the kind of active monitoring needed to identify machine-speed lateral movement and anomalous behavior. As AI changes offensive cyber operations, government and industry should reconsider whether current compliance models produce enough real defensive capability.
The Cyber Game Has Changed
The meaningful change is not that AI can write a phishing email or scan a website. The change is that offensive agents can act persistently after access, make decisions across complex environments, and compress what once took human operators weeks into minutes or seconds.
Organizations should challenge assumptions built around the way cyber operations used to work. Detection must become a first-class capability. Defenders need automation that can operate continuously. Compliance programs must be evaluated not only by whether a control exists, but also by whether the organization can see and respond to an adversary moving at machine speed.
DCG remains deeply focused on compliance, but we are also developing practical, secure defensive mechanisms for the AI era. The threat environment is changing quickly. Our defensive model must change with it.